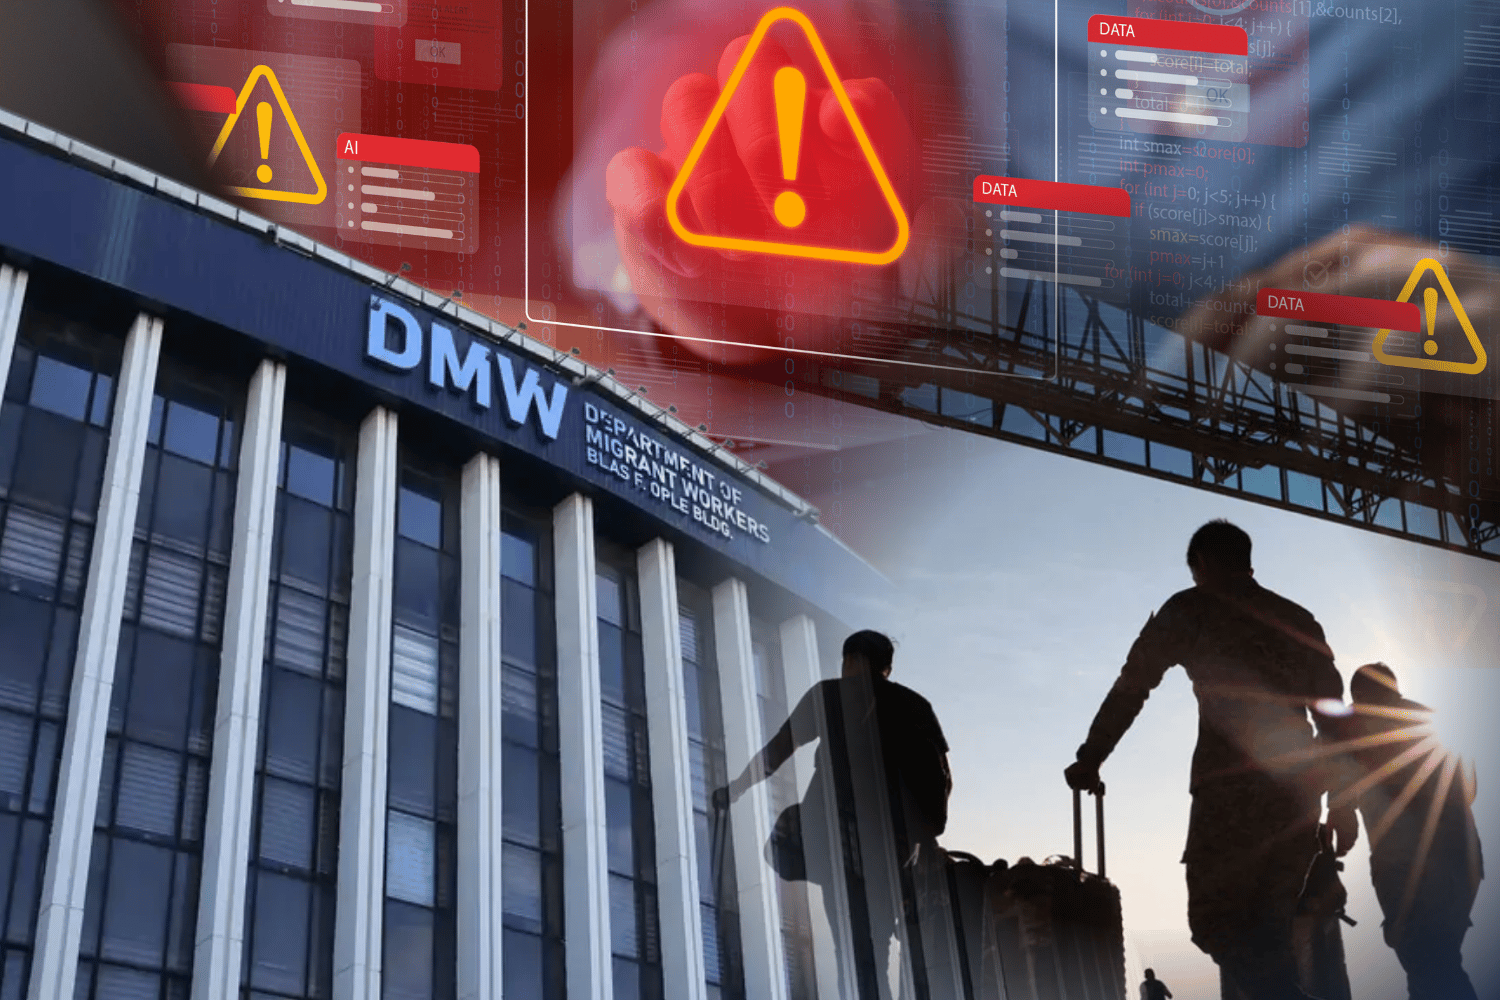
The NPC will investigate the incident to check for Data Privacy Act violations.
What the files contain — and whether migrant workers were affected — remains unclear.
The National Privacy Commission is investigating reports that an operator copied database backups linked to government overseas-employment systems. The Commission said it is coordinating with the Department of Migrant Workers (DMW) to assess the incident and safeguard data subjects’ rights.
The investigation follows an Oct. 28 report by cybersecurity firm Hunt.io. The firm said it recovered logs showing that 27 Microsoft SQL Server backup files, totaling 68.837 GB, were copied on Sept. 6 in 23 minutes and 46 seconds. Their filenames refer to systems associated with the Philippine Overseas Employment Administration and overseas Filipino workers. The POEA’s functions have since been integrated into the DMW.
The potential impact depends on what the backups contain and whether personal information was exposed. The filenames point to databases associated with employment processing, help desks, contracts, and repatriation. If the backups contain workers’ personal records and unauthorized parties can access them, that information could potentially be misused—for example, in scams targeting OFWs. Those risks have not been confirmed.
Hunt.io said it did not examine the backups, so their contents remain unverified. Its report also did not establish where the copied files went, how the operator initially gained access, or whether malicious tools found on the exposed server were run on government systems.
The NPC’s investigation will assess the facts and determine whether any violations of the Data Privacy Act of 2012 occurred. The reported 68GB is the size of the backup files; it is not a confirmed count of affected people or exposed records.
As radar’s business editor, Kenneth oversees stories on innovation, enterprise, and business trends. Off the clock, you’ll find him jamming to Mariah Carey, logging miles on a run, or diving for a volleyball.